- Oct 12, 2026
- 10 min read
Building Effective AML Transaction Monitoring Rules
Discover how AML transaction monitoring rules catch suspicious activity, cut false positives, and keep compliance teams audit-ready in 2026.

In March 2026, FinCEN fined a global broker-dealer $80 million, the largest penalty ever imposed on a broker-dealer under the Bank Secrecy Act. Over six years, the firm ran an inadequate AML program and failed to file at least 160 required Suspicious Activity Reports.
Penalties are becoming harder to avoid. Financial crime is growing more sophisticated, AI-driven fraud is changing what suspicious activity looks like, and regulators worldwide are raising expectations. Compliance teams need monitoring that catches genuine threats quickly without burying investigators in false positives, and that comes down to well-calibrated rules.
This guide covers the regulatory requirements, common monitoring scenarios, and best practices for building rules that hold up.
What are AML transaction monitoring rules?
AML transaction monitoring is the process of reviewing customer activity and transactions to identify unusual patterns that may indicate money laundering, terrorist financing, or other financial crime.
Transaction monitoring rules define the conditions that trigger alerts for further review, such as transactions that exceed a certain threshold or deviate from a customer’s expected activity. Every time a transaction is made, the enabled rules are automatically applied to determine whether the transaction matches the rule parameters.
Conditions and parameters should reflect the business’s products and services, customer risk profiles, applicable regulatory requirements, and identified financial crime risks.
For example, a typical transaction monitoring scenario might involve a customer who usually makes small domestic transactions but suddenly wires $15,000 to an offshore account in a high-risk jurisdiction and then immediately receives a similar amount from another source. This pattern could trigger an alert under a rule designed to detect unusual activity or potential layering, and prompt further review for money laundering.
Combining rules and scenarios lets businesses prioritize alerts, investigate high-risk cases, and, where required, file Suspicious Activity Reports (SARs) or Suspicious Transaction Reports (STRs) with the relevant Financial Intelligence Unit (FIU).
Suggested read: The Three Stages of Money Laundering: How Placement, Layering, and Integration Work
Why transaction monitoring rules matter
AML transaction monitoring rules automate the detection of suspicious transaction patterns, flagging activity for further review to help prevent money laundering and other financial crime. Calibration is a balancing act. Rules must be sensitive enough to catch genuine suspicious activity, but not so broad that they flood compliance teams with false positives.
Some jurisdictions also mandate additional checks based on specific risk factors. In the UK, for example, businesses must consider certain factors when deciding whether enhanced due diligence applies. These include cash-intensive customers, products or transactions that favor anonymity, links to higher-risk jurisdictions, and transactions involving goods such as oil, arms, precious metals, and precious stones.
Failure to meet country-specific monitoring requirements can lead to enforcement action, including fines, license restrictions, and even license loss. Depending on applicable law and the circumstances, responsible individuals may also face personal liability. In the UK, for instance, failing to disclose knowledge or suspicion of money laundering in the regulated sector can be a criminal offense under section 330 of the Proceeds of Crime Act 2002 (POCA), subject to the statutory conditions and exceptions.
Suggested read: AML Odyssey: How Growing Businesses Find Their Way to Ithaca
AML transaction monitoring guidelines for 2026
Effective AML transaction monitoring should reflect applicable regulatory requirements and key global standards such as those issued by the FATF (Financial Action Task Force). FATF’s July 2026 report highlights the role of public-private collaboration in exchanging strategic information, such as financial crime typologies, red flags, and risk trends. This can then feed into transaction monitoring rules to improve detection and reporting of suspicious activity.
Global transaction monitoring regulations
The FATF Recommendations have helped shape AML rules worldwide, yet the exact legal requirements for transaction monitoring vary by country. Some key examples include:
- EU. Currently, obliged entities must scrutinize transactions throughout the customer relationship, keep customer data up to date, and file suspicious transaction reports with their national FIU, under national laws implementing the AML Directive 2015/849, as amended. However, the new EU AML Regulation creates a single rulebook that will generally apply from July 2027. This establishes harmonized requirements for risk-based ongoing monitoring and prohibits anonymous bank, payment, and crypto-asset accounts. The Anti-Money Laundering Authority (AMLA) is expected to start directly supervising selected high-risk cross-border institutions from 2028.
- US. Ongoing monitoring is required to detect and report suspicious activity under applicable sector-specific rules. For banks, SARs are generally due within 30 days of initial detection of facts that may constitute a basis for filing, with up to 60 days permitted if no suspect is identified. FinCEN’s bank SAR rule generally applies to suspicious transactions involving or aggregating at least $5,000. These rules are established under the Bank Secrecy Act (BSA) and FinCEN implementing regulations (31 CFR Chapter X).
- UK. Firms must conduct ongoing monitoring and scrutinize transactions against their knowledge of the customer, the customer's business, and risk profile, with monitoring scaled to risk. SARs must be submitted to the UK Financial Intelligence Unit (UKFIU), part of the National Crime Agency, "as soon as practicable." Applicable legislation includes the Money Laundering Regulations 2017 and Proceeds of Crime Act 2002.
- Canada. Reporting entities must conduct risk-based ongoing monitoring of business relationships under the Proceeds of Crime (Money Laundering) and Terrorist Financing Act and its regulations. STRs must be submitted to FINTRAC as soon as practicable after completing measures that establish reasonable grounds to suspect a reportable offense. Threshold-based reports cover certain transactions worth CAD 10,000 or more. These include cash or virtual currency received in an amount equivalent to CAD 10,000 or more. They also include qualifying international electronic funds transfers (EFTs) of CAD 10,000 or more. The rules may require adding multiple transactions within a 24-hour period. Specific requirements and exemptions depend on the sector.
- Australia. The AML/CTF Act 2006 and AML/CTF Rules require entities to monitor customer transactions as part of their AML program. Suspicious matter reports are generally due within 3 business days, or within 24 hours for terrorism financing suspicions. Threshold transaction reports cover transactions involving A$10,000 or more in physical currency, and international funds transfer instruction reports are also required.
- Singapore. Under the Corruption, Drug Trafficking and Other Serious Crimes (Confiscation of Benefits) Act and sector-specific MAS Notices (e.g., MAS Notice 626 for banks), institutions must conduct ongoing monitoring and scrutinize transactions for consistency with their knowledge of the customer, the customer’s business and risk profile, and, where appropriate, source of funds. They must also pay special attention to complex, unusually large, or unusual patterns of transactions with no apparent economic or lawful purpose. STRs must be submitted to the Suspicious Transaction Reporting Office as soon as reasonably practicable.
- Mexico. Rules are set out in sector-specific laws (e.g., Article 115 of the Credit Institutions Law) and general AML provisions issued under those laws. Institutions must have systems to detect unusual activity and submit reports required under applicable sector-specific rules, including Relevant Transaction Reports, Unusual Transaction Reports, and Internal Operations of Concern reports. Reporting deadlines vary by sector and report type, with specified cases requiring a 24-hour Unusual Transaction Report.
Risk-based approach
The risk-based approach (RBA) is a core principle of the FATF Recommendations and is reflected in national anti-money laundering and counter-terrorism financing (AML/CFT) regulations around the world. US FinCEN’s proposed reforms, published in April 2026, explicitly state that “AML/CFT programs should be risk-based, with more financial institution attention and resources directed toward higher-risk customers and activities, consistent with the risk profile of a financial institution, rather than toward lower-risk customers and activities.”
In transaction monitoring, RBA involves tailoring monitoring intensity to identified risks, with closer scrutiny of higher-risk customers and transactions.
Integrating Customer Due Diligence (CDD) and Know Your Customer (KYC) processes also builds a foundation for transaction monitoring. This includes verifying customer identities, understanding their expected activity, and keeping customer information and risk assessments up to date.
Modern AML strategies also rely on perpetual KYC (pKYC), ongoing monitoring, and dynamic risk scoring, where customer risk levels can shift in real time based on new behaviors, transaction patterns, or external data. Automated tools and AI analytics help here, picking up complex laundering patterns that static rules can miss.
Suggested read: Transaction Monitoring in AML: Ultimate Guide
AI and machine learning in rule-based monitoring
Rules alone struggle to detect increasingly sophisticated money laundering schemes, which can involve high transaction volumes and subtle indicators of suspicious activity. A traditional rule-based approach also lacks the flexibility to capture evolving patterns and may generate large volumes of false positives.
AI transaction monitoring tools can learn a customer's typical behavioral baseline, then flag deviations that fixed thresholds would miss while suppressing alerts on routine activity that generates the most false positives.
Explainability is an important consideration for AI tools. Explainable Artificial Intelligence refers to AI systems' ability to provide clear, comprehensible rationales for the decisions they make and the actions they take. This is an important part of robust AI model governance, which should also include controls to ensure models are validated and their decision-making processes are documented. The EU AI Act provides a right to explanation for certain decisions involving specified high-risk AI systems.
Monitoring real-time and instant payments
Instant payment systems are now available in over 70% of jurisdictions worldwide, with Visa projecting that alternative payment methods, including real-time payments, will account for 58% of e-commerce transactions by 2028. While instant payments are highly convenient for users and businesses, they can challenge transaction monitoring because they leave little time to identify and respond to suspicious activity. Monitoring systems need to process transactions, flag suspicious activity, and, where appropriate, trigger automated responses in real time.
Suggested read: Scaling Payments Across Latin America: Fraud, Compliance, and Local Rails
Red flags in transaction monitoring
Effective transaction monitoring starts with defining red flags that may signal money laundering or terrorist financing. Organizations should consider the following indicators when establishing transaction monitoring rules:
1. Geographical risk indicators
- Transactions involving high-risk jurisdictions: Transfers to or from jurisdictions with significant AML/CFT deficiencies or high exposure to corruption, organized crime, or other criminal activity.
- Use of offshore jurisdictions: Transfers to or from numerous offshore jurisdictions without a clear business or economic rationale.
2. Transaction behavior indicators
- Potential structuring: Splitting funds into multiple smaller transactions in a pattern that may indicate an attempt to evade reporting requirements.
- Rapid movement of funds: Deposits followed by immediate withdrawals or transfers, especially when inconsistent with the customer's known profile.
- Unusual transaction size or frequency: Large or frequent transactions inconsistent with the customer’s known or expected business activity or financial profile.
3. Customer profile indicators
- Linked customer activity: Transfers between, or coordinated transaction patterns across, accounts of apparently unrelated customers sharing the same address, phone number, or IP address.
- Activity following profile changes: A sudden increase in transaction value or frequency following changes to the customer’s profile (contact details, ownership, etc.).
- Activity inconsistent with age: Transaction values or frequency that are unusual for the customer’s age group.
4. Account activity indicators
- Dormant account reactivation: An inactive account suddenly resumes activity with substantial transactions that differ from its historical patterns.
- Unusual activity in new accounts: A newly opened account shows unusually high transaction values or frequency compared with the customer’s expected activity.
Detecting payment errors
Transaction monitoring isn’t only about crime. The same system can run rules that catch everyday payment errors before they turn into customer complaints. A rule can flag payments with mismatched account numbers or currencies before they fail or end up in the wrong place. It can also spot the same charge appearing twice within minutes, often caused by a glitch or an automatic retry, so the customer can be refunded quickly. Missing or invalid details, like a blank tax ID or an incomplete address, can trigger a request for verification or a pause on the transaction until the data is fixed.
Preventing account takeovers
Companies can also use transaction monitoring rules to spot signs that criminals have taken over an account. Suspicious transaction activity that might indicate an account takeover includes:
- A sudden change in the volume and/or value of transactions
- New transactions from or to accounts flagged for criminal activity or located in high-risk jurisdictions, inconsistent with the customer’s usual activity
- Frequent changes in payment information followed by unusual transactions
Building rules for regulatory compliance
Monitoring rules can also enforce other compliance obligations, such as:
- Screening customers and transactions against applicable sanctions lists (e.g., OFAC, OFSI, EU, UN), assessing potential matches, and taking required action, such as rejecting transactions, freezing assets, and reporting to the relevant authorities
- Applying additional checks, such as biometric authentication, if suspicious behavior is detected
- Using blockchain analytics to help assess risks associated with crypto transactions
- Adding Travel Rule functionality to support compliance with applicable requirements to collect and transmit originator and beneficiary information
For example, in the US, a financial institution must report cash transactions exceeding $10,000, subject to applicable exemptions. It could set an AML rule that flags repeated cash deposits or withdrawals below the $10,000 currency transaction report threshold within a defined period, as this may indicate structuring.
Criminals can move funds through multiple accounts or transactions to obscure their origin, a process known as layering. To help detect this, an AML rule could, for instance, compare incoming and outgoing transactions and flag incoming funds followed shortly by withdrawals or transfers of similar amounts.
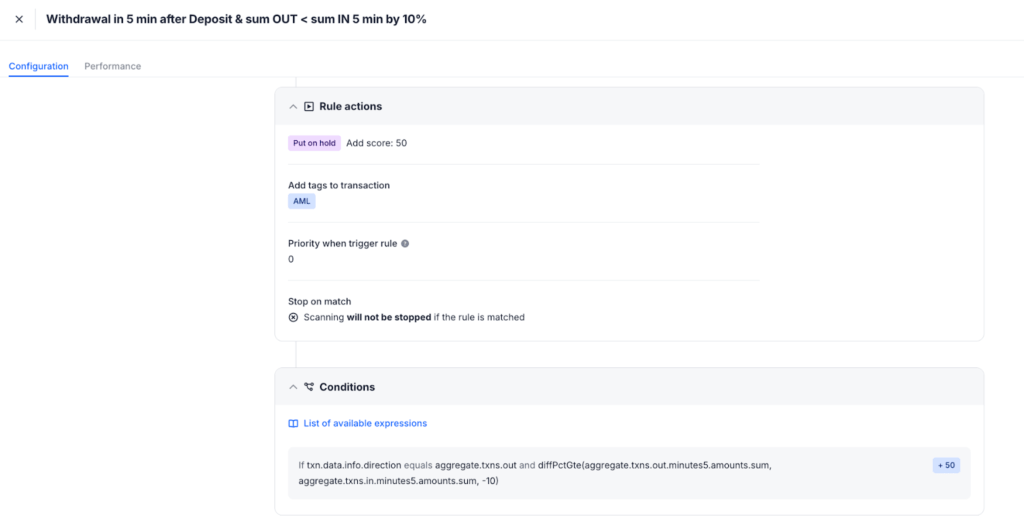
This rule can then trigger one or both of the following automated actions:
- Requesting information or supporting documents about the source and destination of funds
- Assigning a tag to the customer’s profile to highlight the previous alert when further transactions occur
Suggested read: AML Red Flags: Common Indicators, Industry Examples, and Detection Best Practices
How to build and calibrate monitoring rules
Building effective rules is an iterative process, not a one-time configuration exercise. The following should help:
- Start with your risk assessment. Map rules to the specific typologies your customer base, products, and geographies expose you to, rather than deploying generic templates.
- Set thresholds using real transaction data. Back-test proposed thresholds against historical activity to estimate alert volume before going live.
- Segment by customer type. A threshold appropriate for retail customers may generate excessive false positives or miss real risks when applied uniformly to business accounts.
- Monitor rule performance and investigation outcomes. Assess alert volumes, false positives, and the usefulness of alerts to investigations, using metrics such as alert-to-SAR conversion rates.
- Review rules regularly. Regulators increasingly expect teams to document how they regularly review and update AML rules.
- Layer AI on top of static rules. AI can detect anomalies that fixed thresholds may miss and maintain auditability through appropriate documentation and audit trails.
Common mistakes in transaction monitoring rules
Even well-resourced compliance teams can make these mistakes:
- Copying rules from another jurisdiction or provider. Rules that aren’t adapted to your risks and tested on your own data either flood teams with false positives or miss relevant typologies.
- Treating thresholds as permanent. Customer behavior, products, and payment rails change, and thresholds need to keep up.
- Ignoring instant payment speed. Batch monitoring can flag a payment only after it has settled, when it’s too late to intervene.
- Applying fiat rules to crypto. Crypto transaction monitoring also needs blockchain analytics to trace on-chain flows and spot exposure to illicit wallets and services.
- Under-documenting rule rationale. Without records, it’s hard to show supervisors why a rule exists, how its parameters were set, and whether it works.
- Keeping fraud and AML teams apart. Cases that span both, like an account takeover followed by laundering of the stolen funds, can slip through without shared information.
Best practices for AML, KYC, and CDD
To build a strong AML framework, institutions should adopt several best practices:
- KYC/CDD: Identify customers and verify their identities, assess customer risks, and keep customer information up to date. Apply ongoing due diligence throughout the business relationship.
- Transaction monitoring: Use automated systems to analyze transaction patterns, flag suspicious activity, reduce false positives, and improve detection.
- Coordinated governance: Establish clear responsibilities for reviewing and approving rule changes and model updates. Document decisions and use monitoring outcomes and SAR/STR quality reviews to improve controls.
Perpetual KYC and ongoing due diligence
Customer risk can change quickly, so a one-off KYC check at onboarding isn’t enough: pKYC reassesses risk when something changes instead of waiting for a scheduled review. Triggers include an unusual transaction pattern, a new sanctions or PEP screening match, or a change in ownership structure.
Perpetual KYC works well with real-time transaction monitoring. When a rule detects a sudden change in behavior, it can update the customer’s risk score, tighten their monitoring thresholds, or request new source-of-funds documents.
Choosing an AML transaction monitoring solution
As a business grows, manual review stops scaling. A good AML transaction monitoring solution combines rules with AI, handles large transaction volumes in real time, and frees investigators to focus on the alerts that matter.
Sumsub’s AML Transaction Monitoring solution offers:
- A library of 600+ rules for fintech, crypto, trading, iGaming, and other industries, plus no-code tools to build your own.
- AI anomaly detection that picks up complex laundering patterns static rules can miss.
- Built-in case management with analytics and reporting tools for investigations, FIU reports (e.g., STRs), and audits.
- Real-time alerts via webhooks, so your team can review flagged transactions as soon as they happen.
AML transaction monitoring rules FAQ
-
What are transaction monitoring rules?
Transaction monitoring rules are criteria that allow companies to spot potentially suspicious transactions. Companies can configure rules to reflect their risk exposure across customers, products, and geographies, accounting for applicable regulatory requirements.
-
What are transaction monitoring scenarios?
Transaction monitoring scenarios describe activity patterns that rules are designed to detect. Common examples include:
- Repeated cash transactions below reporting thresholds that may indicate structuring
- Incoming funds followed shortly by withdrawals or outgoing transfers of similar amounts
- Transaction amounts or frequency inconsistent with the customer’s known or expected activity
- Sudden substantial activity in a previously dormant account
- Coordinated transfers across apparently unrelated customer accounts
- Unusual transaction activity involving higher-risk customers
-
What are transaction monitoring alerts?
Transaction monitoring alerts flag potentially suspicious activity for review. An analyst checks each alert and, if it warrants a closer look, investigates whether there are grounds to suspect money laundering or other financial crime. Suspicious cases are escalated to the Money Laundering Reporting Officer or another designated compliance officer, who decides whether to file a SAR or STR with the relevant FIU. If they decide not to file, the reasons should be documented.
-
What is a false positive AML alert?
A false positive AML alert occurs when activity is flagged as potentially suspicious but, after review, does not raise suspicion. Companies can reduce false positives by tailoring monitoring scenarios to their risk exposure, calibrating thresholds, and regularly reviewing rule performance.
Relevant articles
- Article
- 3 days ago
- 8 min read
Discover how charity money laundering works, spot red flags, and apply AML best practices to protect against financial crime.

- Article
- 1 week ago
- 10 min read
New account fraud and fraud beyond onboarding differ in timing, signals, and risk. See how AI-powered detection tackles both fraud types.

What is Sumsub anyway?
Not everyone loves compliance—but we do. Sumsub helps businesses verify users, prevent fraud, and meet regulatory requirements anywhere in the world, without compromises. From neobanks to mobility apps, we make sure honest users get in, and bad actors stay out.
